PHP2Shell Vulnerability: What Business Leaders Need to Do This Week


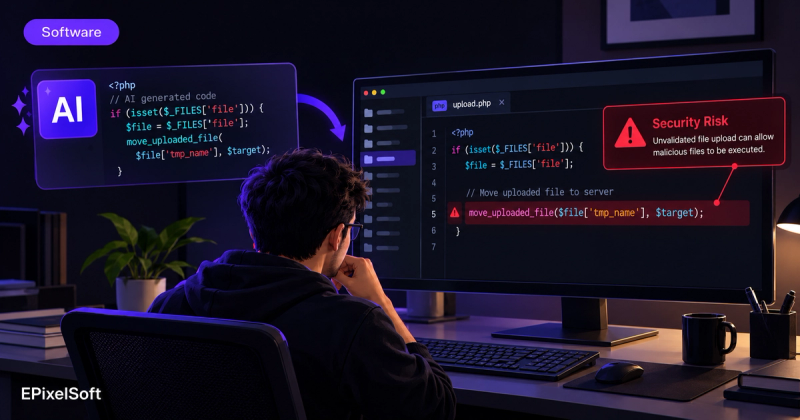
PHP2Shell is the name for two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619, disclosed on 21 October 2026 with a CVSS v4.0 score of 9.2 each. They allow unauthenticated remote code execution on web servers running PHP 5.4 through 8.5. Fixes shipped in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Older branches get no official release. Fintech and SaaS leaders running PHP applications should confirm their runtime version, patch supported branches, restart every worker process, and plan migration off end-of-life versions.
On 21 October 2026, the PHP project shipped emergency fixes for two flaws in the language runtime itself. In the two days before the fix landed, government sites across Europe went dark. Finland pulled its public services offline. According to The Register, 32 UK government services became unavailable and four more were partly disrupted, figures the tech minister gave the House of Lords.
Most of those outages were precautionary. The minister told the Lords there was no confirmed compromise of central government systems. The UK's National Cyber Security Centre had advised organisations that could not patch immediately to consider taking systems offline, and the US National Security Agency gave the same advice. Those were sound defensive calls by competent teams. They also show how little room this patch window leaves.
Attackers were early too. Amazon Threat Intelligence reported that its MadPot honeypot network logged an exploitation attempt on 17 October, four days before public disclosure. If your business runs PHP, assume probing has already started.
Why a Fully Patched Application Can Still Be Exposed
Think of your application as the vehicle and PHP as the engine. Your developers built the vehicle. They did not build the engine, and PHP2Shell sits in the engine. The security.com analysis makes the same point: a fully up-to-date application can still be exposed when the runtime beneath it is not. A clean code review does not change that.
The reach is enormous. W3Techs reports PHP on 69.3% of websites whose server-side language is known, and Wiz puts the affected share of the internet at roughly 70%. WordPress, Drupal, Joomla and phpBB all run on it, as do control panels and appliances that embed PHP without saying so. Calif, Wiz and Cloudflare all place the exposure at PHP 5.4 and later, which spans more than a decade of releases.
How the flaws surfaced matters as much as what they do. Calif found the first one in August using OpenAI's GPT-5.6 Sol during an audit funded through OpenAI's Patch the Planet programme. Wiz independently found both with Gemini 4 Argon, GPT-5.6 Sol and its own Wiz Atlas tool, and said a single researcher with frontier models finished in a week what once took an expert team months. Calif offered a sober counterpoint: knowing PHP's history mattered more than the model.
About The Author
Anil Kothiyal
LinkedInAnil Kothiyal is the Founder and CEO of EPixelSoft, an AI-native software engineering firm with 12 years and 700+ products shipped across FinTech, HealthTech, NGO operations, and SaaS. He has led engineering engagements for clients across the US, UK, Africa, and Asia — including platforms that compressed underwriting cycles from days to hours and field reporting systems deployed in East Africa. Anil writes about AI in production, high-stakes software delivery, and what it actually takes to build systems that hold up at scale.